
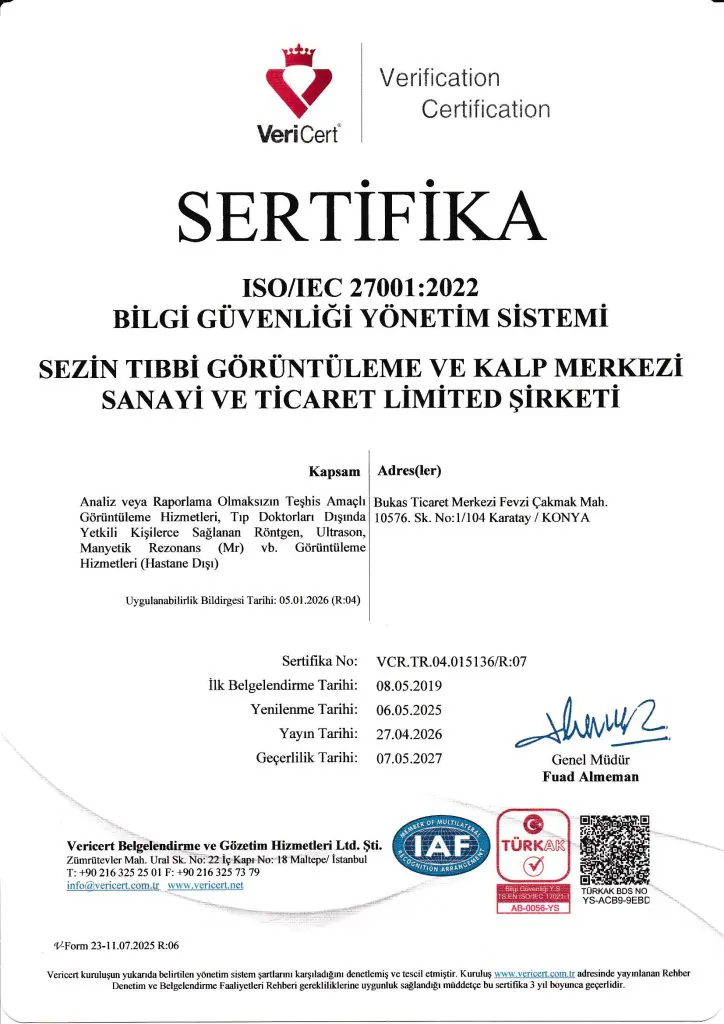
 ISO 27001:2022Information Security Management System
ISO 27001:2022
Information Security Policy
Our TS EN ISO 27001:2022 Information Security Management System aims to demonstrate that information security management is ensured, and to safeguard risk management, across people, infrastructure, software, hardware, organisational information, third-party information and financial resources in all operations within the scope of Information Technologies — starting from the contract review stage and covering tendering, business development and project design, procurement, service delivery, technical service provision and all related operations.
Accordingly, the objectives of our ISMS Policy are to:
- Continually improve the Information Security Management System
- Manage information assets; determine the security values, needs and risks of assets; and develop and implement controls addressing security risks
- Define the framework of methods for identifying information assets, their values, security needs, vulnerabilities and the frequency of threats
- Define a framework for assessing the impact of threats on the confidentiality, integrity and availability of assets
- Establish the working principles for risk treatment
- Continuously monitor risks by reviewing technological expectations within the scope of the services provided
- Meet information security requirements arising from national and international regulations, legislation, agreements and corporate responsibilities
- Reduce the impact of information security threats to service continuity and contribute to continuity
- Have the competence to respond rapidly to information security incidents and minimise their impact
- Maintain and improve the level of information security through a cost-effective control infrastructure
- Enhance the organisation’s reputation and protect it from adverse effects related to information security
- Ensure the continuity of the Information Security Management System